


When a Thailand or ASEAN operation adopts AI document creation, fluent prose is not the deciding factor. The real test is whether the company can explain who created an investment request, management report, SOP or customer-facing document; which inputs and template version were used; who approved it; and what evidence supported the released version. This guide does not cover a standalone email writer or proposal generator. It focuses on one controlled foundation across business documents: input classification, approval, provenance, versioning, Thailand PDPA and cross-border processing, RFP requirements, a 30/60/90-day proof of concept, and acceptance evidence.
The operating principle is simple: AI is not the person who completes the document. It is a drafting step that works from governed evidence and templates. A human with the right authority releases the document, and the released file carries an evidence ID. With that structure, the company can add document types without rebuilding governance each time.
Decide the document workflow before selecting an AI writing tool
A demonstration is easy. Upload last month’s report and ask for the new one in the same style. In seconds, the result looks credible. Operational questions then appear:
- May the source report contain employee names, customer details, prices or equipment incidents?
- Which system and cut-off time supplied the sales, quality and delivery figures?
- Which of the Japanese parent version and Thai or English derivative is current?
- Who catches a regulation or customer requirement that the model invented?
- How is the PDF sent to the customer distinguished from a Word file edited later?
- Can the company reconstruct the inputs, sources, approval and issued version during an audit or claim?
Prompt technique does not answer these questions. Break document creation into intake, drafting, review, approval, release and retention, then assign responsibility and evidence at every stage. Use our generative AI implementation guide for ASEAN manufacturing sites for the organisation-wide roadmap and this article for the controlled document layer.
Four document families should not share one identical approval path
A common platform is useful, but uniform treatment is not. Route each document according to purpose, recipient, error impact and data content.
| Document family | Typical sources | Main impact of error | Suggested final approver | Evidence retained at release |
|---|---|---|---|---|
| Investment request / internal approval | Quotations, purpose, TCO, budget, delegation policy | Poor investment, authority breach, overspend | Department head plus value-based authority | Quote versions, calculation, route, approval time |
| Monthly / management report | ERP, MES, quality, inventory, previous issue | Wrong decision and inconsistent reporting | Metric owner plus site leader | Extraction time, report/query ID, reconciliation |
| SOP / work instruction | Equipment specification, process limits, risk assessment, change request | Safety, quality incident, obsolete instruction | Process owner plus quality/safety | Parent version, change reason, training, effective date |
| Customer submission / proposal / RFP response | Customer request, approved specifications, price, schedule, contract terms | Contract exposure, loss of trust, leakage | Sales owner plus engineering/legal/management | Compliance matrix, exceptions, evidence, sent copy |
These approvers are examples, not a legal rule. Align them with the company’s delegation of authority, quality system, safety rules and customer contracts. The important point is to name accountable people independently of whether AI is used. Too many new “AI approvals” create queues; no approval creates unauthorised releases.
Build the enterprise document workflow in eight stages
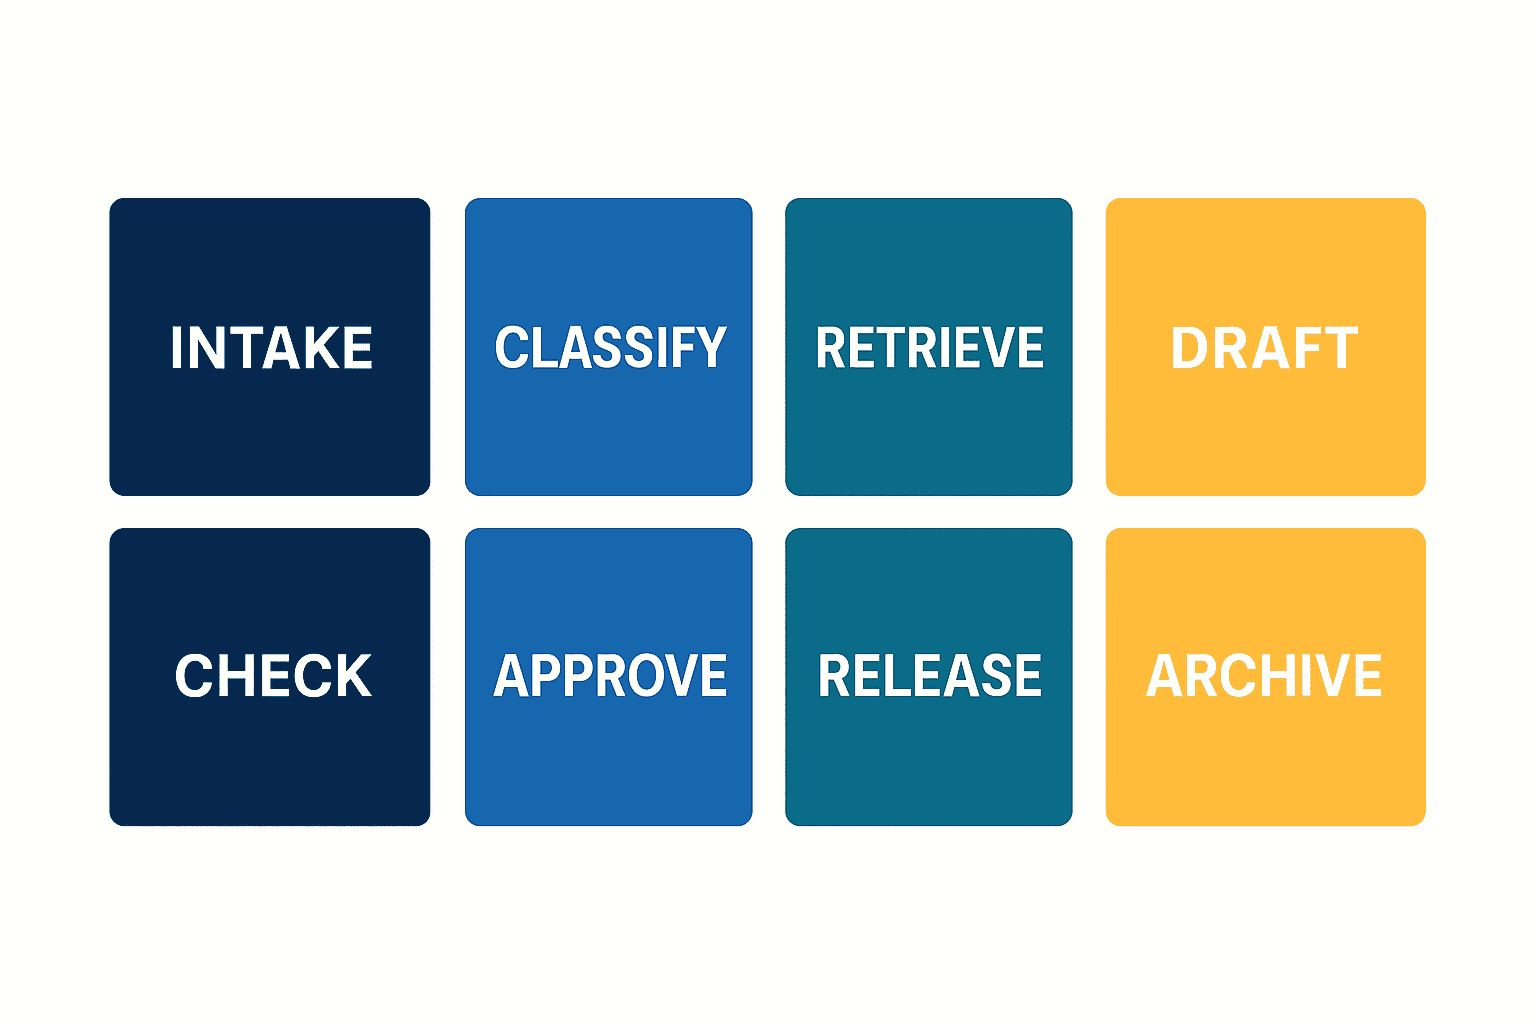
1. Intake and document-type classification
Do not begin with a blank box saying “create a report.” Require the requester to select document type, period, recipient, language, confidentiality and deadline. The system can flag file types, personal data, customer secrets and possible controlled information. Automated classification supports, but does not replace, the requester’s declaration and control-owner review.
2. Data minimisation and permission check
Remove employee IDs, signatures, personal bank accounts, health data, private customer contact details and other fields unnecessary for the purpose. Pseudonymise with case IDs or roles where appropriate. Ask not only “may this go to AI?” but “may this field be used for this purpose, and could processing occur outside Thailand?”
3. Retrieve approved evidence
Pull the required content from approved ERP reports, MES records, quality documents, contracts, specifications and current SOPs. Attach document ID, version, effective date, page or section, retrieval time and owning department. If the PDF is scanned, OCR and field validation are separate prerequisites. Our practical AI-OCR guide for Thailand explains why document quality and field-level acceptance need their own controls.
4. Fix the template and generation conditions
A controlled template carries its version, mandatory headings, prohibited statements, language, units, date format and glossary. Govern the prompt through template ID, model and settings, citation rules, no-specing and missing-information behaviour. If evidence is missing, return “confirmation required”; do not fill the gap with a plausible sentence.
5. Draft with AI
The model may summarise, structure, translate and normalise expression within the supplied evidence. It should display calculation inputs and formulae. External facts appear only with a valid source. For an SOP, it must not invent safety conditions or control limits. For a customer submission, it separates supported, exception and confirmation-needed responses rather than smoothing uncertainty into a promise.
6. Automated checks and human review
Automated checks cover mandatory fields, numerical reconciliation, units, prohibited wording, customer identity, confidentiality marking, expired sources and differences from the parent version. A business owner reviews substance; quality, legal or security specialists review their domains where required. Record checklist results and comments, not merely “reviewed.”
7. Approval and release
The approver sees a release candidate together with differences, evidence list and unresolved items. After approval, the system fixes the PDF or other controlled format and adds document number, version, effective date, approver and evidence ID. A post-approval content change creates a new version and returns to approval; it does not silently overwrite the issued file.
8. Retention, withdrawal and feedback
Retain the issued file, references to source inputs, generation conditions, model output, human edits, approvals and delivery event. Avoid duplicating raw inputs unnecessarily, and define retention and deletion ownership. Corrections and rejections improve the evaluation set only after permission to reuse personal or confidential content has been checked.
Start input classification with Public, Internal, Confidential and Restricted
An elaborate taxonomy is likely to be ignored. Map to the existing information-classification policy and begin with four usable tiers.
| Tier | Examples | Illustrative AI input rule | Required controls |
|---|---|---|---|
| Public | Published web pages, catalogues, government documents | May use in approved service | URL, retrieval date, revision check |
| Internal | General work notes, non-sensitive procedures, anonymised results | Enterprise-contracted environment only | SSO, access, retention, audit log |
| Confidential | Cost, pricing, customer specifications, unreleased product, incident detail | Only after use case, provider and region approval | DPA/contract, encryption, minimisation, output control |
| Restricted | Sensitive personal data, credentials, export-controlled or privileged content | Prohibited by default; exception through DPO/legal/security | Isolated environment, case impact assessment, strict log |
This is an implementation example, not a statutory classification. “No personal data” does not mean “safe”: drawings, prices, recipes and incident reports can be protected by contract. Conversely, masking a name may not anonymise a person if job title, time and a rare incident make identification possible.
The intake form should require data owner, presence of personal data, customer confidentiality, purpose, intended recipients, storage and possible foreign processing. Embedding the decision into the work request is more practical than asking every employee to interpret a long policy.
Provenance and version control stop plausible errors
Generative AI errors are dangerous because they can be credible. Do not treat provenance as a list of URLs at the end. Link each important claim to evidence.
Fields in an evidence record
source_id: unique ERP report, contract, SOP, web source or record keyowner: department accountable for source correctnessversionandeffective_datelocator: page, section, cell, record key or extraction conditionretrieved_at: timestamp with time zonepermitted_use: internal summary, customer submission, translation and so onretention: period for the reference copy and generation log
If a monthly report says sales were THB 12.5 million, “from ERP” is insufficient. Retain company, period, currency, tax treatment, credit-note handling, closing status and extraction time. If an SOP specifies torque, cite the approved specification or process-condition version and section. If a customer document promises a delivery date, point to the approved plan or contract response, not somebody’s recollection.
Trace the complete document lineage
Connect request ID, input snapshot, template version, prompt version, model/settings, model-output version, review differences, approval event and delivery event to the issued version. There is no need to store hidden model reasoning. Reproducibility requires what was supplied, the controlled generation conditions, the returned draft, human changes and the final authorisation.
Treat translations as derivatives, not disconnected copies. If Japanese SOP v3.2 produced Thai v3.2-TH and the parent becomes v3.3, the Thai derivative automatically becomes “review required.” Changes to safety, numeric limits, tools, PPE or inspection frequency are not minor wording edits.
Evaluate Thailand PDPA and cross-border processing by data flow
“Is cloud AI compliant with the PDPA?” is too broad to answer. Give legal and the DPO a concrete data-purpose-party-location-retention description.
| Question | What the impact assessment and RFP should fix |
|---|---|
| Data | Personal fields, sensitive categories, customer secrets, pseudonymisation |
| Purpose | Summarisation, translation, drafting, search or quality check |
| Parties | Controller, processor, sub-processors, affiliates, users |
| Locations | Storage, inference, logs/backups and support access |
| Retention | Inputs, outputs, audit logs, evaluations and backups |
| Transfer route | Applicable Section 28/29 route, contract, BCR or exception to confirm |
| Rights support | Search, export, correction and deletion capabilities |
| Incident handling | Detection, notice, evidence preservation and responsibilities |
Thailand’s government PDPA FAQ explains that a cross-border transfer may constitute disclosure and should be assessed with the legal basis and notice obligations as well as Sections 28 and 29. For intra-group transfer, an approved Binding Corporate Rules route may be relevant. The ASEAN–EU joint guide describes ASEAN Model Contractual Clauses and EU Standard Contractual Clauses as voluntary model provisions that may be incorporated into cross-border arrangements. A clause does not remove the need to map the transfer and evaluate applicable law and supplementary safeguards.
A provider statement that data is not used for training matters, but it answers only one question. OpenAI states that business products and API inputs and outputs are not used to train models by default. Retention, processing location, residency, sub-processors and Zero Data Retention eligibility still differ by product, endpoint and contract. OpenAI’s 19 August 2026 announcement describes ZDR for eligible API customers as no retention of prompts or responses after a request is processed. Fix the applicable DPA, product terms, sub-processor list, storage/inference region, retention and support access in the RFP and contract.
This is not legal advice. Thailand PDPA, employment rules, customer contracts, sector rules and cross-border conclusions depend on the facts. Confirm the current PDPC/MDES materials with Thailand counsel and the DPO.
Turn an internal generative AI policy into a decision table
“Do not enter confidential information” and “always check the answer” are too vague. A usable internal guideline specifies the approved service, input tier, document approval, prohibited use, incident route and log handling.
At minimum, include:
- Covered people, entities, languages and devices.
- Approved AI services, accounts, features and connections.
- Permitted input tiers and masking/deletion rules.
- Approvers by document family and releasable formats.
- Verification of AI-generated numbers, citations, laws, standards and customer requirements.
- Parent/translation synchronisation and glossary ownership.
- Stop-and-report procedure for secret input, wrong release or misinformation.
- Retention and deletion of logs, inputs, outputs and evaluation data.
- Exception request path, expiry and authority.
- Review on a quarterly cycle and whenever models or contracts change.
A prohibition-only policy drives shadow AI. Explain the safe route and where to ask. Maintain semantically aligned Japanese, Thai and English versions with named translation owners.
Measure report automation separately from writing quality
An automated report is not accepted because it reads well. Measure source completeness, close status, calculations, period-on-period variance, provenance and approval time.
| Dimension | Example measure | Acceptance evidence |
|---|---|---|
| Input completeness | Requests with every mandatory dataset | Intake log and missing-data reason |
| Numeric integrity | Match between closed ERP/MES values and release | Automated reconciliation and sample recalculation |
| Evidence coverage | Important claims carrying a valid source_id | Claim-to-source map |
| Correction load | Fields/words changed by humans and reason | Version diff and correction category |
| Approval time | Intake to release and number of returns | Timestamps and approval log |
| Release control | Unapproved external deliveries | DLP/delivery log and incidents |
An illustrative PoC could require zero disagreement in approved figures, 100% evidence coverage for critical claims and zero restricted inputs. These are proposed gates, not legal or industry thresholds. Management, business owners, DPO and quality should set them for the document risk.
Combine this with our 30/60/90-day AI impact measurement guide to connect approval lead time, rework, erroneous releases and labour to an investment decision rather than reporting log-in counts.
Make the compliance matrix central to AI proposal creation
A proposal-only generator can produce polished prose while omitting a customer requirement or making an unapproved promise. Treat proposals as one customer-document workflow and keep the requirements compliance matrix as the authoritative record.
For each requirement, retain:
requirement_id, original text, received version and page;- interpretation and clarification question;
- response type: standard, custom, exception, out of scope or confirmation needed;
- evidence: product specification, engineering answer, quotation, plan or contract term;
- owner across sales, engineering, legal and management;
- location in the proposal; and
- approval state and expiry.
AI can classify, retrieve similar answers, draft and normalise. Authorised people approve price, date, performance commitment, liability, third-party product and site conditions. Block release when the RFP response conflicts with the proposal or any requirement remains unanswered.
Put these 12 requirements into the AI document RFP
- Document scope: departments, languages, volumes and exclusions for approvals, reports, SOPs and customer submissions.
- Input classification: detection, blocking and pseudonymisation for personal, customer and restricted data.
- Model/service control: models, change notice, settings, fallback and stop procedure.
- Data flow: storage, inference, logs, backup, support access and sub-processors in one diagram.
- Retention/deletion: periods and deletion evidence for prompts, outputs, embeddings, logs and evaluations.
- Provenance: source ID, version, locator, citation, expiry and inherited source permissions.
- Template/version control: parent, language derivatives, effective date, withdrawal and reapproval.
- Workflow: roles, segregation, amount/document gates, delegation, timeout and return.
- Checks: numbers, units, forbidden claims, evidence, personal data and multilingual quality.
- Audit trail: who input, generated, edited, approved, released and sent what and when.
- Integration/exit: IdP/SSO, ERP/MES/DMS, email, APIs, complete export and deletion on exit.
- Operations/SLA: incident, model change, vulnerability, support languages, training and improvement.
Do not accept “supported” without evidence. Ask for configuration screens, API specifications, sample logs, sample deletion certificates, incident notice, sub-processor list and data-flow diagram. Confirm whether PoC templates, tests and evaluation data can move to production and be exported at contract end.
Convert NIST, ASEAN and ISO into implementation checks
NIST AI RMF’s Govern, Map, Measure and Manage functions apply directly. Govern establishes ownership and policy; Map classifies documents, inputs, recipients and impact; Measure tests provenance and prohibited input; Manage runs approval, release, incident response and improvement.
The Expanded ASEAN Guide organises generative AI governance across nine dimensions, including Accountability, Data, Trusted Development and Deployment, Incident Reporting, Testing and Assurance, Security and Content Provenance. For document automation, the value is their connection in one operational workflow rather than isolated accuracy testing.
ISO/IEC 42001:2023 addresses establishing, implementing, maintaining and continually improving an AI management system for organisations that provide or use AI. ISO/IEC 42005:2025 provides an impact-assessment approach covering intended and unintended effects. This article does not claim conformity or certification; these standards help connect a pilot to management review and continual control.
| Framework element | Document-platform deliverable |
|---|---|
| NIST Govern | AI policy, RACI, approval authority, exceptions |
| NIST Map | Document register, data flow, recipients, impact assessment |
| NIST Measure | Evidence match, numeric match, bad citations, returns, prohibited input |
| NIST Manage | Release gate, stop, incident response, improvement backlog |
| ASEAN Content Provenance | Source ID, template version and issued-version lineage |
| ISO/IEC 42001 / 42005 | Objectives, impact assessment, audit and management review |
A 30/60/90-day PoC for the controlled foundation

Days 1–30: measure documents and data
Select one workflow from each of the four document families. Collect recent examples with appropriate handling, then measure creation time, returns, data source, approval and errors. Inventory templates, glossary, versions, owners and storage.
Deliver a document register, input classification, data-flow map, baseline, impact/risk assessment, RACI and PoC test plan. Decide what may be entered and who may release before debating the model.
As a proposed starting point, use 20 cases per family, 80 total. This is not a standard. Increase rare, exception-heavy SOP and customer-RFP cases; reduce highly repetitive reports. Always include low-frequency, high-impact failures.
Days 31–60: test governed drafting and approval
Use an enterprise-contracted environment. Connect classification, source retrieval, template, drafting, automated checks and approval. Begin with public or anonymised data, then expand only after legal/DPO approval. Test one document across Japanese, Thai and English for parent-version changes, terms, numbers and forbidden expressions.
Do not only compare with a good reference answer. Test refusal when evidence is absent, exclusion of obsolete versions, denial of an unauthorised source and prevention of unapproved delivery. Run the same evaluation before and after model or retrieval changes.
Days 61–90: complete RFP, UAT and handover
Give shortlisted vendors the same flow, evaluation set and exception scenarios. Compare evidence-backed RFP responses. UAT includes obsolete SOP, conflicting figures, unauthorised access, transfer-condition change, model update, mistaken delivery, deletion request and outage.
The day-90 exit is not autonomous production release. It is an approved scope, passed tests, known residual risk, operational ownership, training, incident process and next investment decision. Keeping higher-risk documents in draft-only mode while expanding low-risk ones is a valid success.
Retain these UAT acceptance records
| Scenario | Illustrative pass condition | Evidence retained |
|---|---|---|
| Obsolete SOP mixed into search | Stop release or use only current version | Retrieval log, version decision, warning |
| ERP and spreadsheet conflict | Flag for confirmation; never choose silently | Input snapshots and discrepancy log |
| Customer specification outside role | Deny retrieval, display and generation | Role setting, denial log, retest |
| Unsupported legal statement | Require source or suppress claim | Draft, check result, revision history |
| Unapproved email delivery | Delivery impossible | Workflow and DLP/mail log |
| Deletion request | Find and act on in-scope data | Item list, deletion record, exception reason |
| Model update | Re-run baseline and approve difference | Model version, result, approval |
| Incident/outage | Notify, stop and preserve evidence per procedure | Timeline, notice, recovery, corrective action |
An average pass rate can hide a critical failure. A critical gate fails on one event; minor conditions use thresholds. Requiring zero unauthorised disclosures, zero unapproved deliveries and zero errors in approved figures is a reasonable proposal, not a statutory threshold. Set actual conditions from contract, quality, safety and customer impact.
An evidence pack contains test-case ID, input tier, expected and actual result, operator, timestamp, model/settings, logs, defect, retest and approval. Do not rely only on screenshots; use document and API IDs that survive interface changes.
Calculate cost and value beyond drafting minutes
Cost includes licences/API, retrieval, OCR, integration, SSO, logs, templates, evaluation, legal work, training, operations, regression tests after model changes, maintenance and exit export. Multilingual SOPs also require glossary and parent-version maintenance.
Value includes less drafting, but also fewer transcription errors, returns, obsolete versions, unanswered requirements, approval queues, audit preparation and faulty releases. A simple decision formula is:
Annual net value = labour released + rework avoided + evidence-based expected loss avoided - annual operations - reevaluation and training
Do not inflate avoided loss without evidence for likelihood and impact. If evidence is weak, show it as residual risk rather than money. Measure end-to-end intake-to-release time, including data preparation, checking, return and approval—not only seconds spent generating text.
Review this operating dashboard every month
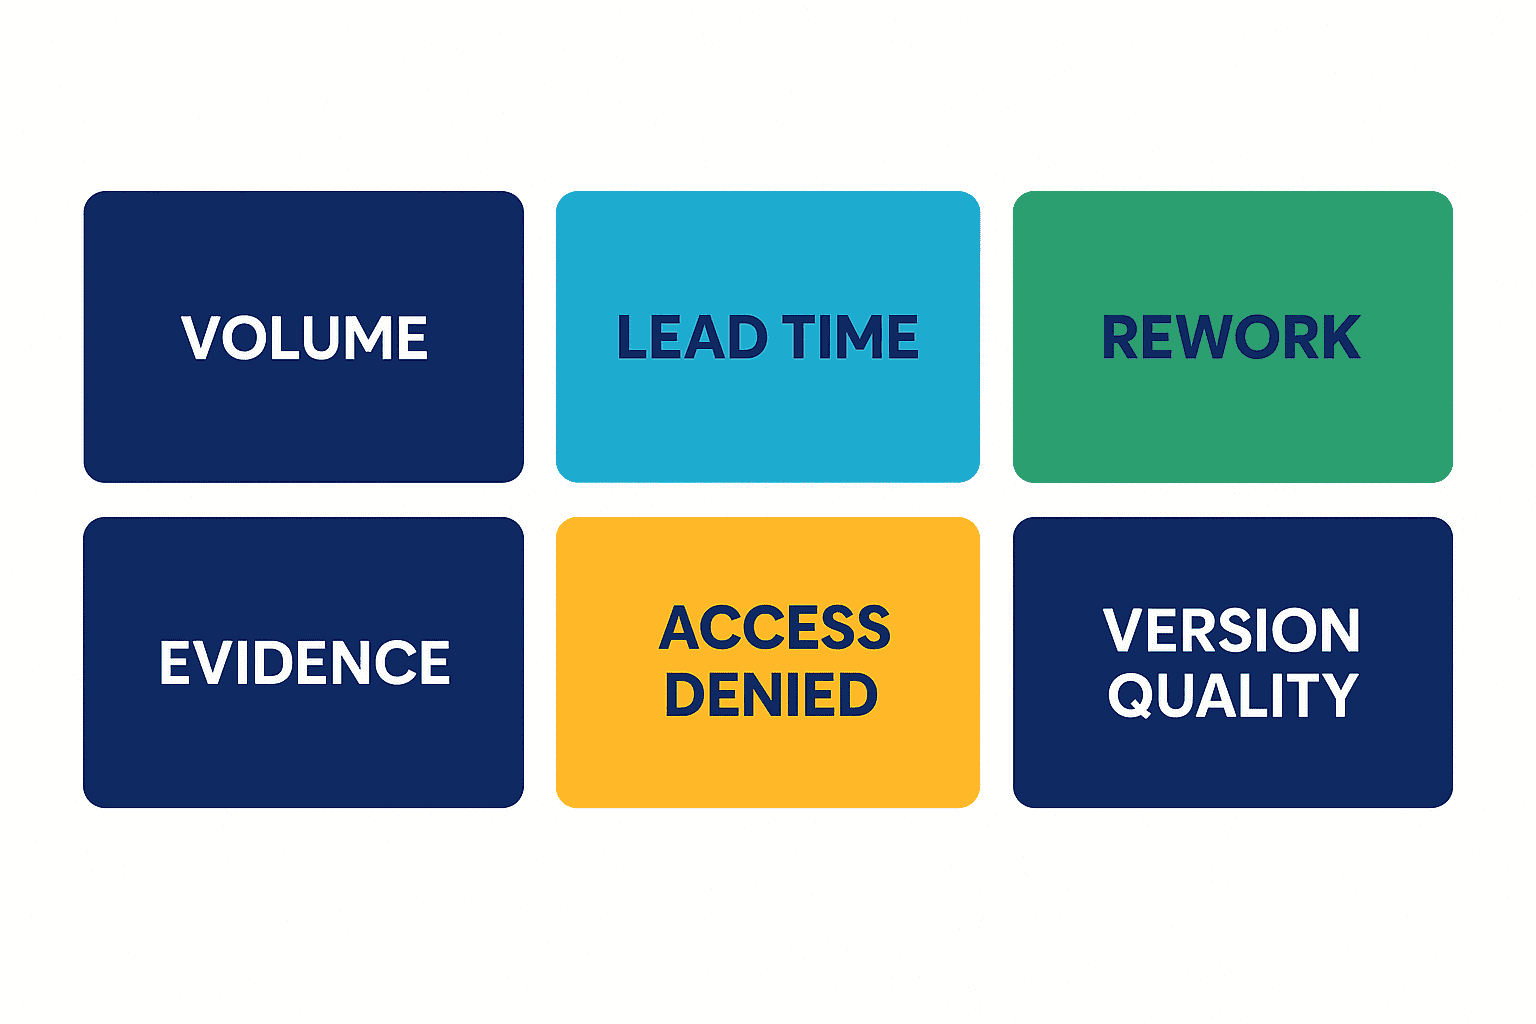
- Requests, releases and unfinished work by document family.
- Intake-to-draft, draft-to-approval and approval-to-release time.
- Return reason: missing input, evidence, number, translation, permission or wording.
- Unsupported critical claims, expired sources and obsolete-version references.
- Human edit volume and why AI suggestions were rejected.
- Prohibited inputs, access denials, blocked misdelivery, incidents and exceptions.
- Quality by model, template, prompt and glossary version.
- Use and value by document family, language and department.
Usage is not success. Confirm that safe use, shorter approval lead time and stable critical-error levels occur together. If users return to personal tools, first fix speed, language coverage and missing templates in the approved route.
Common failure modes and controls
Give everyone a general AI account, then write policy
The company cannot recover prior input or see what was released. Implement approved accounts, minimum classification and logs for a small scope first.
Save drafts and issued files in the same shared folder
Files called “final” and “final2” multiply and an unapproved version is sent. Separate working and release repositories; create a released file only from approval.
Put a list of URLs at the end
Nobody knows which source supports which statement or whether revision invalidated it. Store claim, evidence, version and locator structurally.
Manage Thai SOP separately from its Japanese parent
The plant continues with an old condition. Maintain the derivative link and trigger review, prioritising technical terms, numbers and safety changes.
Approve on “we do not train on your data” alone
Storage, processing, sub-processors, logs, deletion and support access remain unknown. Fix the data flow and contract schedule.
Run PoC only on clean success cases
Production conflicts, missing data, old versions, access boundaries and languages remain untested. Design tests to make the system fail safely.
Frequently asked questions
What is AI document creation?
It uses generative AI to draft, summarise, translate and format text. In enterprise use, the controlled workflow—classification, evidence, template, approval, release and audit log—matters more than the model alone. This article covers one foundation across multiple business documents.
Can AI automatically finalise figures in a management report?
It should not. Fix the authoritative ERP/MES source, close status, extraction time and formula. AI writes the narrative; reconciliation and the metric owner approve the final figures.
How does AI proposal creation avoid missing RFP requirements?
Create a requirements compliance matrix before the prose. Retain response type, evidence, owner and approval for every requirement ID, and block release for missing responses or unapproved commitments.
Does using generative AI for internal documents violate Thailand PDPA?
There is no universal answer. Assess fields, purpose, legal basis, notice, provider, storage/processing, transfer, retention, rights support and contract per data flow. Confirm with Thailand counsel, the DPO and current PDPC materials.
How can an internal generative AI guideline become operational?
Embed approved services, input tiers, document approvals, incident reporting and exceptions into the request screen. Align Japanese, Thai and English wording, train with realistic cases and review logs.
May an AI-generated SOP be issued directly?
No. Safety, quality and equipment conditions must come from approved evidence and be reviewed by process and quality/safety owners. Govern parent, translation, change, training, effective date and withdrawal; use AI for drafting only.
How many documents should a PoC include?
There is no standard number. This guide proposes 20 cases in each of four families as a starting point. Representativeness across normal, exceptional, critical, multilingual, obsolete and unauthorised cases matters more than the count.
What RFP evidence matters most?
Data-flow diagrams, sub-processors and regions, retention/deletion, access-denial logs, claim-to-source mapping, version control, approval/release logs and complete export. Require actual configuration and log samples, not only feature statements.
Conclusion: implement the system that creates approved documents
For AI document creation in Thailand and ASEAN, design input classification, evidence, templates, versions, review, approval, release and audit lineage before multiplying tools for investment requests, reports, SOPs and customer submissions. Evaluate PDPA and cross-border issues from a concrete data flow. A 30/60/90-day PoC should test obsolete sources, conflicts, unauthorised access, unapproved delivery, deletion and outage—not only fluent examples—and retain UAT evidence.
TOMAS TECH can help map the document register, input classification, data flow, RFP and PoC/UAT around the ERP/MES, document-management and AI-OCR environment of a Thailand operation. You can consult us while considering just one document family, with the future cross-document foundation kept in view. Contact TOMAS TECH.
References
- OpenAI, Offering Zero Data Retention for frontier models, 19 August 2026: https://openai.com/index/offering-zero-data-retention-for-frontier-models/
- OpenAI, Business data privacy, security, and compliance: https://openai.com/business-data/
- OpenAI, Enterprise privacy, updated 8 January 2026: https://openai.com/enterprise-privacy/
- Thailand Government Contact Center, PDPA FAQ, 17 December 2024: https://gcc.go.th/2024/12/17/%E0%B8%96%E0%B8%B2%E0%B8%A1%E0%B8%95%E0%B8%AD%E0%B8%9A%E0%B8%82%E0%B9%89%E0%B8%AD%E0%B8%A1%E0%B8%B9%E0%B8%A5%E0%B8%AA%E0%B9%88%E0%B8%A7%E0%B8%99%E0%B8%9A%E0%B8%B8%E0%B8%84%E0%B8%84%E0%B8%A5/
- Thailand Ministry of Digital Economy and Society, PDPA laws and notifications: https://mdes.go.th/mission/detail/2319
- ASEAN, Expanded ASEAN Guide on AI Governance and Ethics — Generative AI, 2025: https://asean.org/wp-content/uploads/2025/01/Expanded-ASEAN-Guide-on-AI-Governance-and-Ethics-Generative-AI.pdf
- ASEAN Secretariat / European Commission, Joint Guide to ASEAN MCCs and EU SCCs, 2024: https://asean.org/book/joint-guide-to-asean-model-contractual-clauses-and-eu-standard-contractual-clauses/
- NIST, AI RMF Generative AI Profile, NIST AI 600-1: https://www.nist.gov/publications/artificial-intelligence-risk-management-framework-generative-artificial-intelligence
- ISO, ISO/IEC 42001:2023: https://www.iso.org/standard/42001
- ISO, ISO/IEC 42005:2025 overview: https://www.iso.org/publication/PUB200420.html
This article provides general workflow information, not legal, tax or certification advice. Confirm applicable law, regulation, contracts and data-transfer conditions with the competent authority, local specialists and counterparties using current information.


